Appearance
Return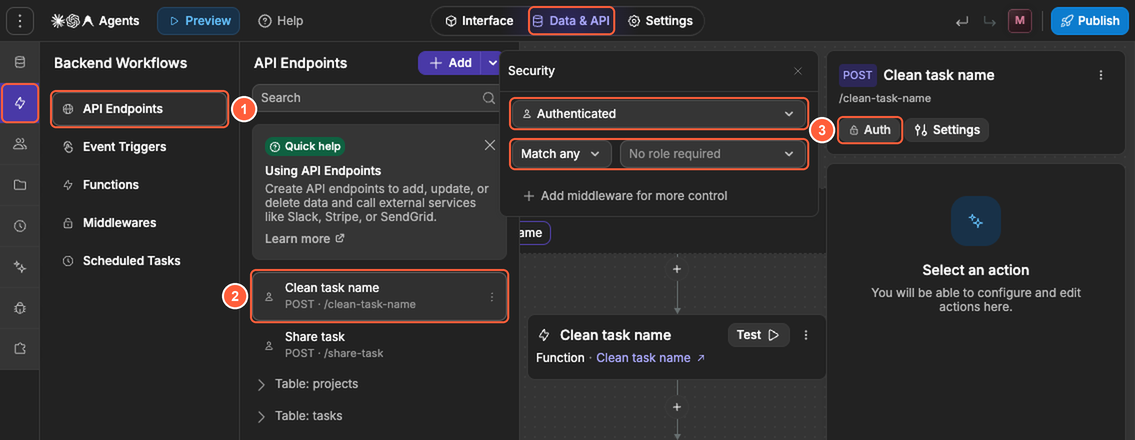
Securing APIs
Protect your APIs so only the right users can access sensitive data.
Steps at a glance
- Create an API from the
API Endpointstab in theBackend Workflowssubtab ofData & API. - Open
Securityon the API endpoint so it requires a signed-in user (and roles if needed). - Test the API in preview mode and confirm it is blocked when signed out.
1) Set Security on the API endpoint
- Open the
Data & APItab, then open theBackend Workflowssubtab and go toAPI Endpoints. - Select your API endpoint.
- Click the access button at the top of the endpoint (it shows
PublicorAuth) to open theSecuritypanel, then set:Publicfor endpoints anyone can access.Authenticatedfor endpoints that require a signed-in user.- Role-based rules when only certain roles should have access: with
Authenticated, chooseMatch anyorMatch all, then select the roles.
2) Return clear responses
When a call is blocked, WeWeb returns an error: 401 if the user is not signed in, 403 if they do not have the required role. Call the endpoint inside a Try/Catch action and show a helpful message in the Catch branch:
- If the user is not signed in, show a helpful message (for example “You must sign in to continue.”).
- If the user is signed in but not allowed, show a message like “You do not have access to this.”
3) Test it quickly
- In preview mode, trigger the API from your interface.
- Test while signed in and while signed out.
- Confirm the result matches your Security settings.
Common pitfalls
Your API works in preview but fails in production
- Check that your production environment uses the same
SSO Providerssettings and environment variables.
You can still access the API from a public page
- Make sure the API endpoint itself is protected with Security settings (not only the page).