Appearance
Return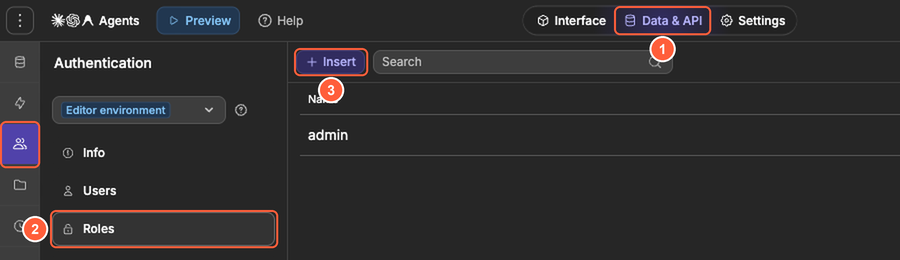
Using user roles
Control what users can see and do by assigning roles and checking them in your app.
Steps at a glance
- Create roles in the
Authenticationsubtab ofData & API. - Assign roles to users.
- Use roles to protect pages and APIs.
1) Create roles
- Open the
Data & APItab, then open theAuthenticationsubtab. - Go to
Roles. - Click
Insert, enter aNamethat matches your needs (for exampleadminormember), then clickInsert.
2) Assign roles to users
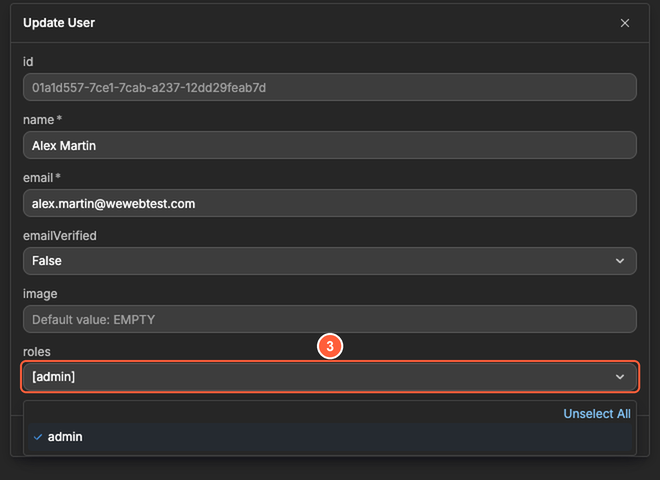
- Open the
Data & APItab, then open theAuthenticationsubtab and go toUsers. - Click the pencil icon next to the user's checkbox to open
Update User. - In the
rolesfield, select the appropriate roles, then clickSave.
3) Use roles in your app
- Protect pages so only certain roles can open them: in the page's
Private accesssettings, setWho can access this pagetoAuthenticated users, then choose the roles inRoles who can access this page. - Restrict table views so only certain roles can retrieve their data: click the access button in the view header, choose
Authenticated, then chooseMatch anyorMatch alland select the roles. - Secure API endpoints with
Securitysettings (and optionalMiddlewaresfor custom role checks) so only allowed roles can access sensitive data.
Learn more about where roles are enforced →
Common pitfalls
A user is signed in but still blocked
- Confirm they actually have the role assigned.
- If you just assigned the role, ask them to refresh the page. Role changes take effect after a refresh.
- Confirm the page or API is checking the same role name.